AI agent security: every agent needs identity, limits and an audit trail
A governance checklist for businesses allowing AI agents to access data and take actions across real systems.
automation changes the threat model
A chatbot that gives a poor answer is a quality problem. An agent that sends the wrong message, changes a record or purchases the wrong item creates an operational incident. As agents chain tools together, a small error can travel quickly through several systems.
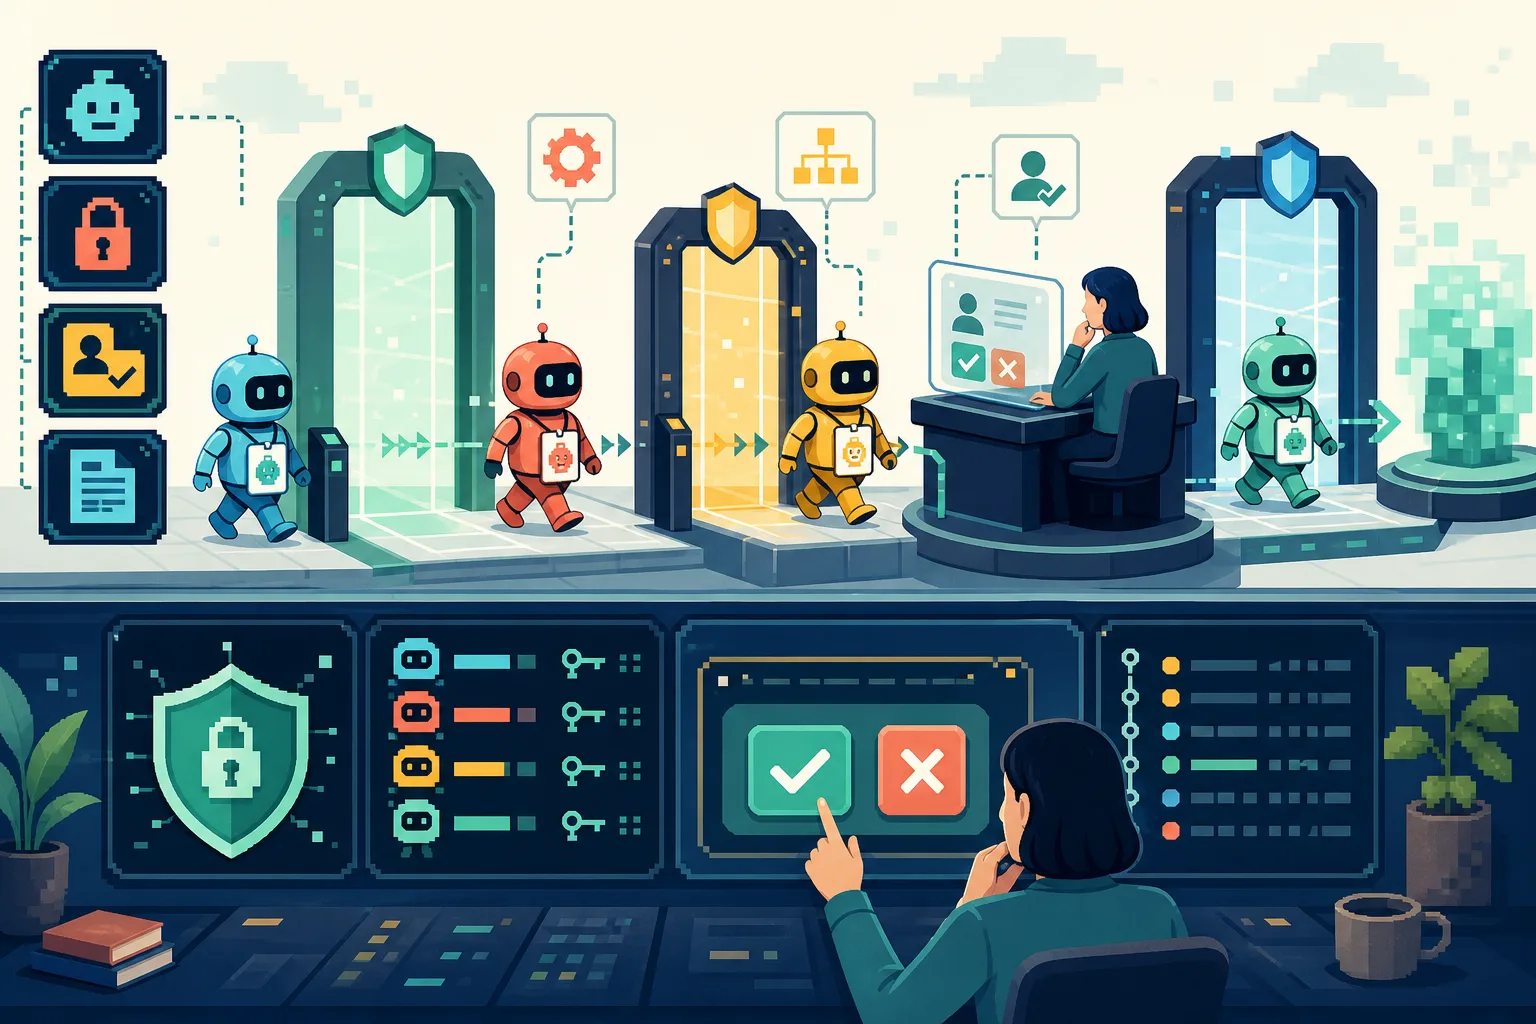
Google Cloud's 2026 forecast calls for discrete boundaries around each agent's authentication, authorization and monitoring. That is the right starting point regardless of vendor.
the minimum control set
Give every deployed agent a unique identity and narrowly scoped credentials. Define which resources it can read, which actions it can propose and which actions require approval. Keep sensitive environments and tools outside reach unless the workflow genuinely needs them.
- allow lists for tools, data and destinations
- spending and volume limits
- human confirmation for irreversible actions
- tamper-resistant logs and alert thresholds
- a fast kill switch and recovery procedure
govern the lifecycle
Review agents when prompts, models, permissions or connected tools change. Test adversarial and ambiguous inputs, not only the happy path. Assign a business owner who understands the workflow and a technical owner who can investigate behaviour.
Governance should make useful automation safer to deploy, not bury it in paperwork. Clear boundaries allow teams to expand successful workflows with confidence.
sources & further reading
make this practical